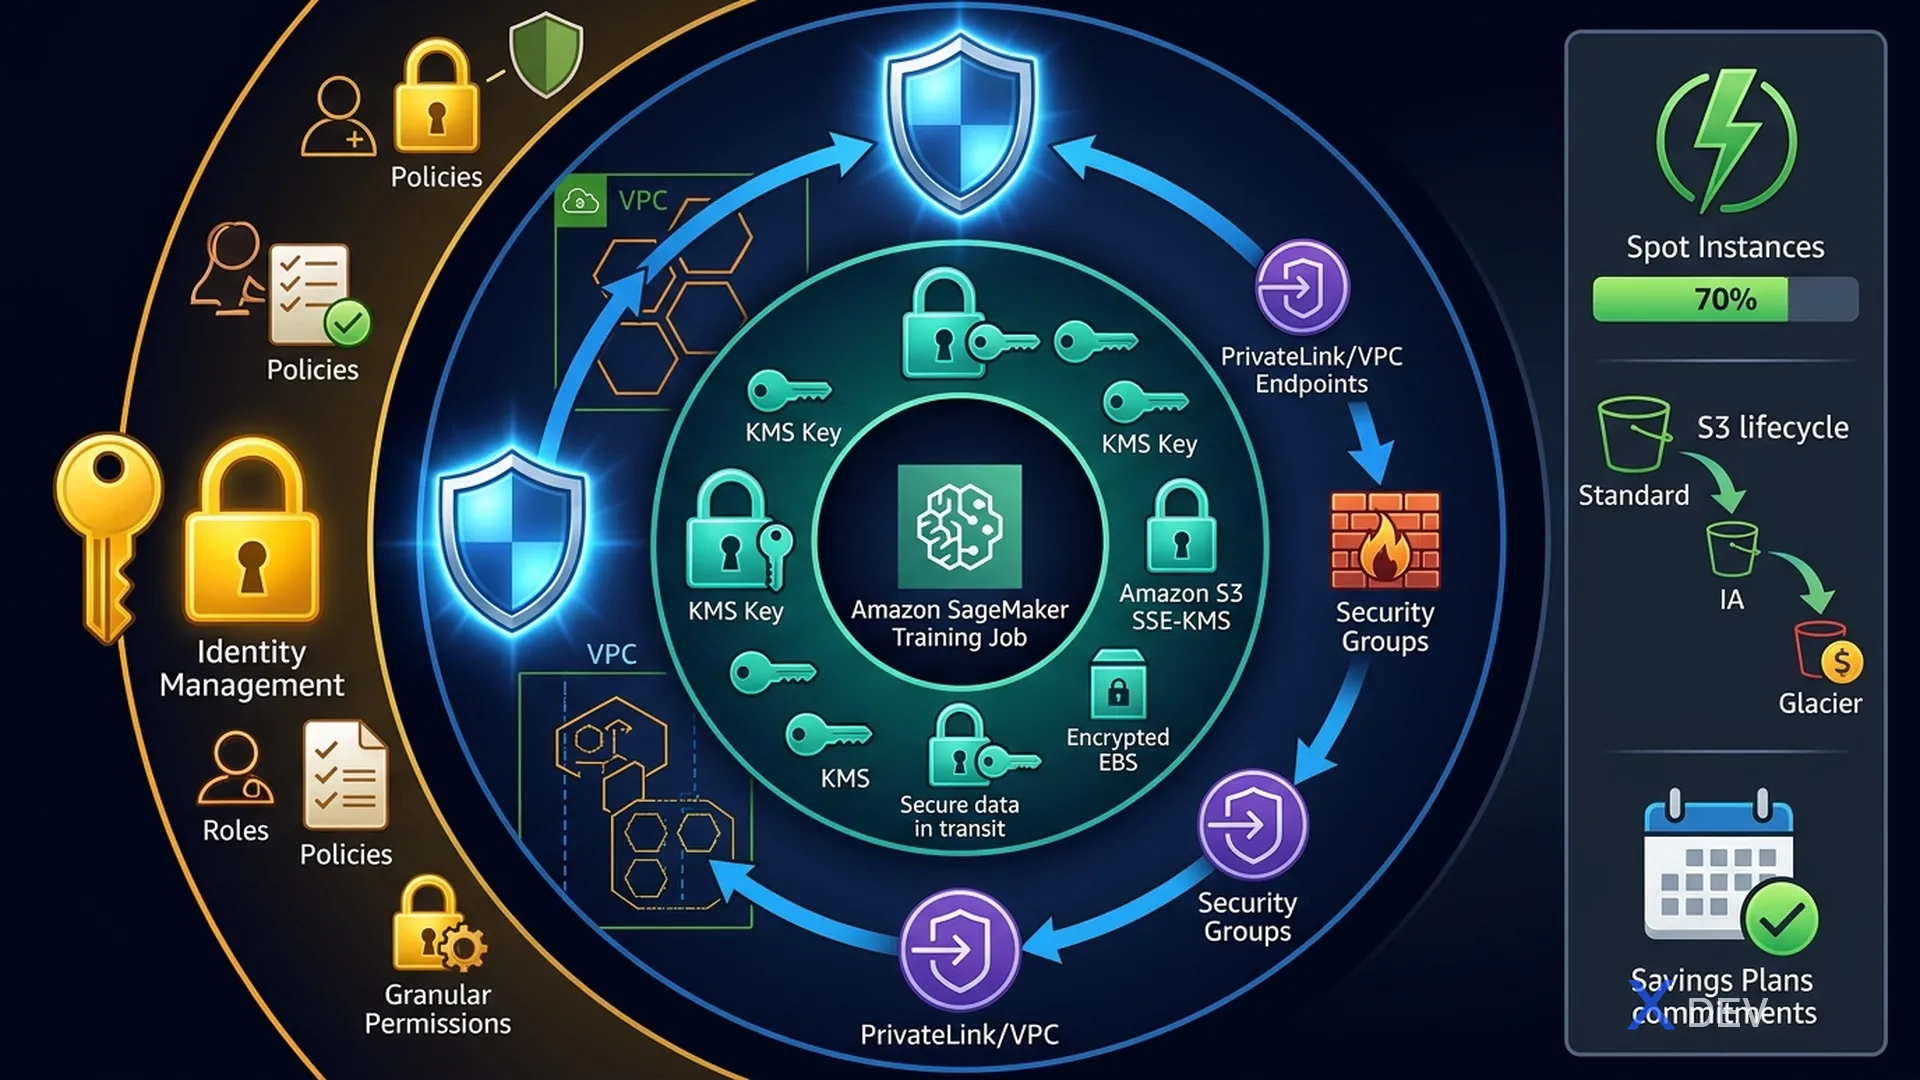
Security trong AWS ML: IAM Roles, VPC isolation, KMS encryption, và tối ưu chi phí với Spot Instances
1. IAM for SageMaker
SageMaker sử dụng IAM Roles (không phải users) để thực hiện actions trên AWS resources. Đây là pattern bảo mật quan trọng trong đề thi.
| Role Type | Used By | Needs Access To |
|---|---|---|
| Execution Role | SageMaker Notebooks, Training Jobs, Endpoints | S3, ECR, CloudWatch, KMS |
| SageMaker Studio Role | Studio IDE users | Data, experiments, pipelines |
| Training Job Role | The training container itself | Input/output S3 buckets |
Exam tip: SageMaker training/inference containers KHÔNG có EC2 instance credentials — họ chạy với IAM Role cross-account. Luôn cần grant S3 và ECR permissions cho execution role.
2. VPC Configuration for SageMaker
Chạy SageMaker workloads trong VPC để đảm bảo traffic không đi qua public internet.
SageMaker Network Security:

Internet ──✗────────────────────────────────────────
                                                    │
          ┌─── Private VPC ──────────────────────┐ │
          │                                       │ │
          │  SageMaker Training Instance          │ │
          │          ↓ (VPC Endpoint)             │ │
          │  ┌──── S3 Gateway Endpoint ────────┐  │ │
          │  │   ECR VPC Endpoint              │  │ │
          │  │   SageMaker API VPC Endpoint    │  │ │
          │  └─────────────────────────────────┘  │ │
          └───────────────────────────────────────┘ │
| Feature | Description |
|---|---|
| VPC Endpoints (PrivateLink) | Access S3, ECR, SageMaker API without internet |
| Security Groups | Control inbound/outbound traffic cho training instances |
| Network Isolation | Training job không có internet access (isolated mode) |
| Inter-Container Encryption | Encrypt distributed training traffic |
3. Encryption
| What | How | Service |
|---|---|---|
| S3 data at rest | SSE-S3, SSE-KMS, SSE-C | S3 + KMS |
| Model artifacts at rest | KMS key cho output S3 bucket | KMS |
| EBS volumes (training) | KMS encryption for instance storage | KMS |
| Data in transit | TLS 1.2/1.3 for all API calls | Default |
| Distributed training traffic | Enable inter-container encryption | SageMaker config |
4. Cost Optimization Strategies
| Strategy | Savings | How |
|---|---|---|
| Spot Instances | Up to 90% | Training Jobs + checkpointing |
| Right-sizing | 20-40% | Match instance type to actual GPU/CPU usage |
| Serverless Inference | Variable | Pay per invocation, no idle cost |
| SageMaker Savings Plans | Up to 64% | Commit to consistent usage |
| S3 Intelligent-Tiering | Variable | Auto-tier old training data |
| Lifecycle Configurations | Variable | Auto-stop idle notebooks |
4.1. S3 Lifecycle Policies cho ML Data
Data Lifecycle for ML:

  Active Training Data (S3 Standard)
           ↓ after 30 days unused
  S3 Intelligent-Tiering
           ↓ after 90 days
  S3 Standard-IA (Infrequent Access)
           ↓ after 180 days
  S3 Glacier Instant Retrieval
           ↓ after 1 year
  S3 Glacier Deep Archive (compliance)
5. Compliance Frameworks
| Framework | Relevance for ML |
|---|---|
| HIPAA | Healthcare ML — PHI data encryption, audit logging, BAA required |
| GDPR | EU data — right to erasure, data minimization, consent |
| SOC 2 | Security controls audit for SaaS ML products |
| PCI DSS | Payment card data in ML models |
6. Cheat Sheet — Security & Cost
| Scenario | Solution |
|---|---|
| SageMaker training with no internet | VPC + Network Isolation + VPC Endpoints |
| Encrypt training data on S3 | SSE-KMS with customer-managed key |
| Reduce training cost by 70%+ | Spot Instances + checkpointing |
| Auto-archive old training datasets | S3 Lifecycle Policies |
| Prevent notebook idle cost | Studio Lifecycle Config → auto-shutdown |
| Healthcare data (HIPAA) | KMS + VPC + CloudTrail + BAA with AWS |
7. Practice Questions
Q1: A company needs SageMaker training jobs to access data in S3 without traversing the public internet for security compliance. What should they configure?
- A) VPC Flow Logs
- B) SageMaker Training with VPC + S3 VPC Gateway Endpoint ✓
- C) IAM policy with IP restriction
- D) AWS Shield
Explanation: Configuring SageMaker Training Jobs to run in a VPC, combined with an S3 VPC Gateway Endpoint, ensures all S3 traffic stays within the AWS network without going through the public internet.
Q2: A machine learning team wants to reduce costs for long-running training jobs that can be interrupted. The jobs should resume from where they stopped. Which approach is MOST cost-effective?
- A) Use larger instances to finish faster
- B) Use Reserved Instances
- C) Use Spot Instances with checkpointing to S3 ✓
- D) Run training locally
Explanation: Spot Instances provide up to 90% cost savings. With checkpointing enabled (saving model state to S3 periodically), jobs can resume from the last checkpoint if interrupted, making Spot Instances practical for long training runs.
Q3: Which AWS service provides centralized key management for encrypting SageMaker training data, model artifacts, and EBS volumes?
- A) AWS Secrets Manager
- B) AWS IAM
- C) AWS KMS (Key Management Service) ✓
- D) AWS Certificate Manager
Explanation: AWS KMS provides encryption key management for at-rest encryption of S3 data (SSE-KMS), EBS volumes used by training instances, and model artifacts. SageMaker integrates natively with KMS throughout the training and deployment workflow.