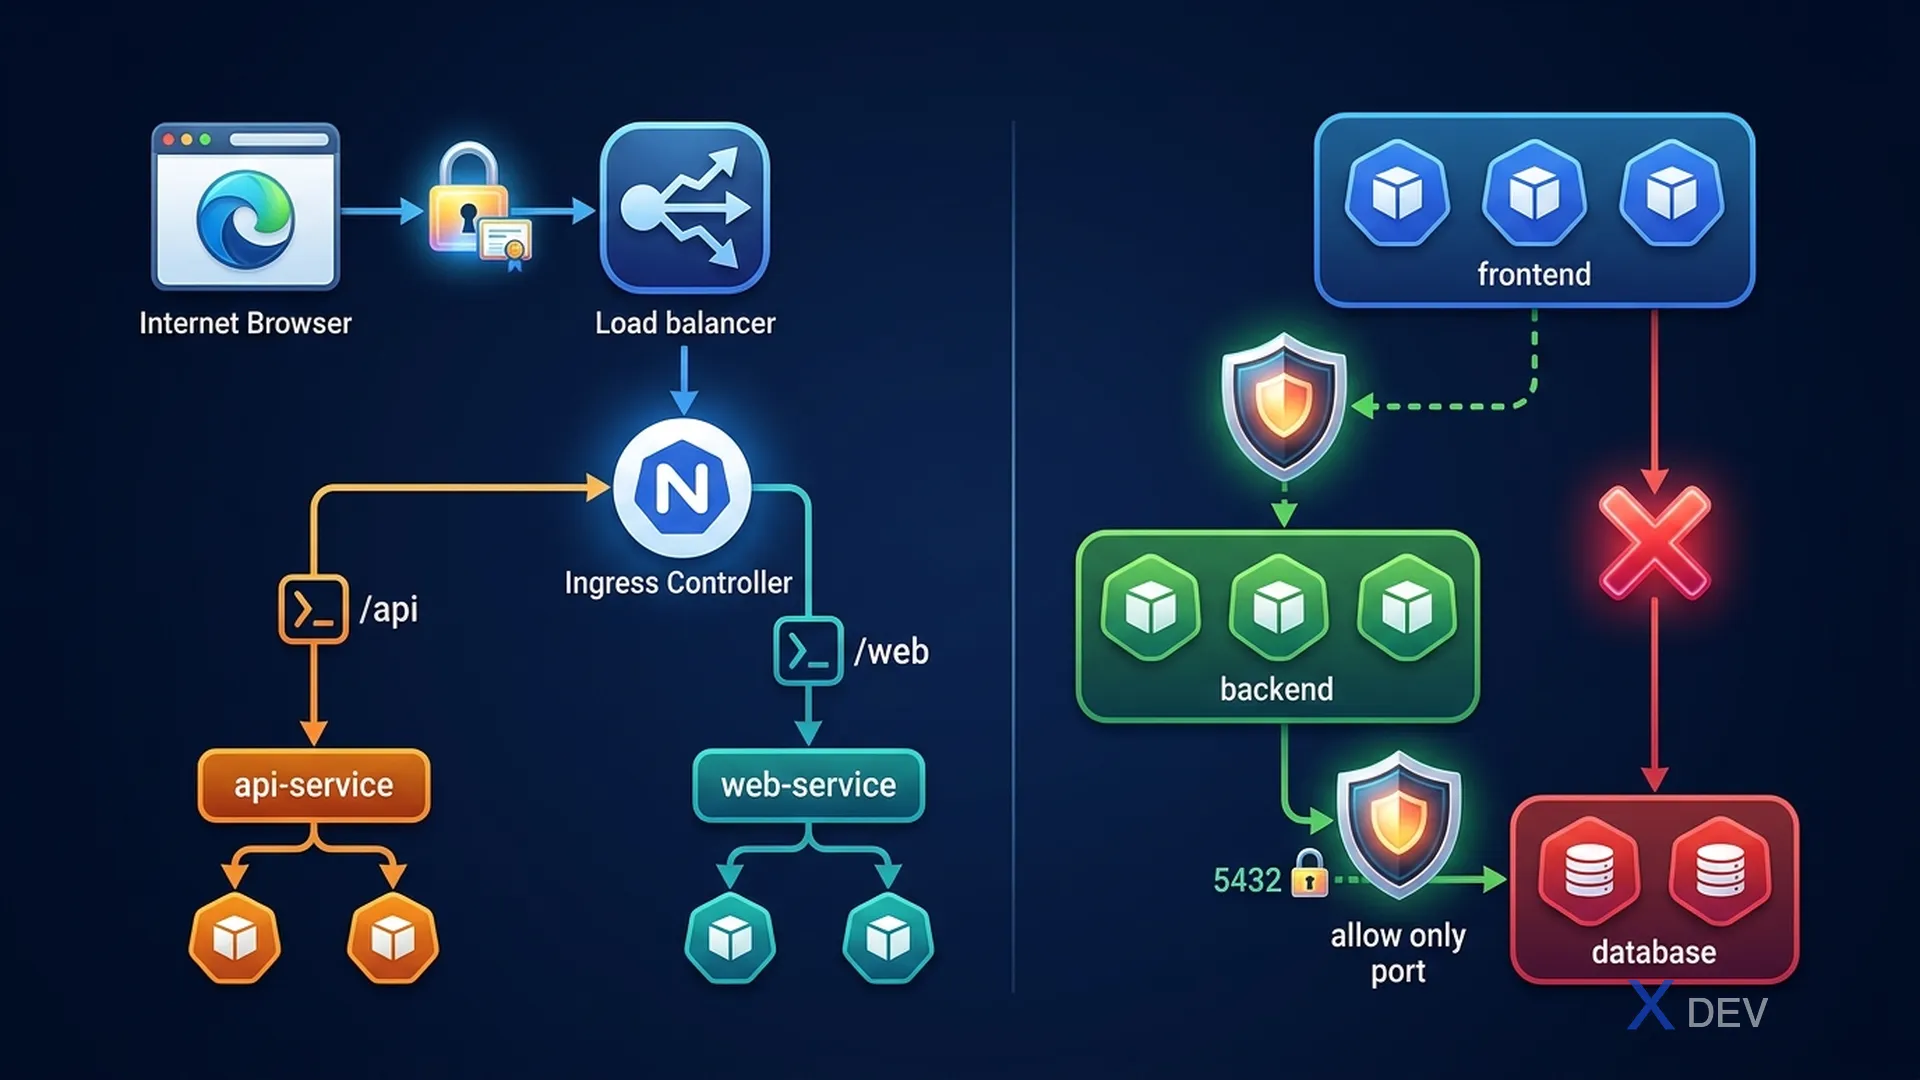
1. Ingress
Ingress cung cấp HTTP/HTTPS routing vào cluster. Cần Ingress Controller (nginx-ingress, Traefik, ALB) để xử lý Ingress resources.
Internet
   │
[Ingress Controller] (nginx Pod, port 80/443)
   │
   ├── /api/* ──────────────► Service: api-svc:8080
   ├── /web/* ──────────────► Service: web-svc:80
   └── shop.example.com ───► Service: shop-svc:3000
apiVersion: networking.k8s.io/v1
kind: Ingress
metadata:
name: app-ingress
annotations:
nginx.ingress.kubernetes.io/rewrite-target: /
spec:
ingressClassName: nginx
rules:
- host: api.example.com
http:
paths:
- path: /
pathType: Prefix
backend:
service:
name: api-svc
port:
number: 8080
tls:
- hosts:
- api.example.com
secretName: tls-secret # TLS cert stored in SecretExam tip: Ingress không hoạt động nếu không có Ingress Controller. CKA exam thường đã có controller cài sẵn. Kiểm tra
kubectl get ingressclassđể xem class name cần dùng trongspec.ingressClassName.
2. Network Policies — CKA Depth
apiVersion: networking.k8s.io/v1
kind: NetworkPolicy
metadata:
  name: allow-frontend-to-backend
  namespace: app
spec:
  podSelector:
    matchLabels:
      app: backend      # Apply to backend pods
  policyTypes:
  - Ingress             # Control incoming traffic
  ingress:
  - from:
    - podSelector:
        matchLabels:
          app: frontend  # Only from frontend pods
    ports:
    - protocol: TCP
      port: 8080

---
# Deny all ingress (default deny)
apiVersion: networking.k8s.io/v1
kind: NetworkPolicy
metadata:
  name: deny-all
spec:
  podSelector: {}     # Select ALL pods
  policyTypes:
- Ingress # No ingress rules = block all ingress| Selector | Ý nghĩa |
|---|---|
podSelector: {} | Select tất cả Pods trong namespace |
namespaceSelector | Cho phép traffic từ specific namespace |
ipBlock | Cho phép traffic từ CIDR range |
3. CNI Plugins
| CNI | Network Policy? | Đặc điểm |
|---|---|---|
| Flannel | Không | Simple overlay, VXLAN/host-gw |
| Calico | Có | BGP routing, high performance, enterprise |
| Cilium | Có (eBPF) | eBPF-based, L7 policies, observability |
| Weave Net | Có | Simple, mesh network |
Exam tip: Calico và Cilium hỗ trợ NetworkPolicy. Flannel không. Nếu exam hỏi "configure network policies" → phải có Calico/Cilium. Trên kubeadm lab, Calico là lựa chọn phổ biến nhất.
4. Pod Network Troubleshooting
# Test pod-to-pod connectivity
kubectl exec -it pod1 -- ping 10.244.1.5
kubectl exec -it pod1 -- curl http://pod2:8080

# Check pod's IP
kubectl get pod pod1 -o jsonpath='{.status.podIP}'

# Check CNI config on node
ls /etc/cni/net.d/
cat /etc/cni/net.d/10-calico.conflist

# Check kube-proxy rules
kubectl get pod -n kube-system -l k8s-app=kube-proxy
iptables -t nat -L KUBE-SERVICES | head -20
5. Cheat Sheet
| Task | Command/Object |
|---|---|
| HTTP routing into cluster | Ingress (+ IngressClass) |
| Block all traffic to a Pod | NetworkPolicy with empty ingress: [] |
| Allow traffic from namespace | NetworkPolicy with namespaceSelector |
| Check CNI plugins | ls /etc/cni/net.d/ |
| Check ingressclass | kubectl get ingressclass |
6. Practice Questions
Q1: You create an Ingress resource but it has no ADDRESS and traffic doesn't route. What is the most likely cause?
- A) The Service type must be LoadBalancer
- B) No Ingress Controller is installed in the cluster ✓
- C) The Ingress must be in the kube-system namespace
- D) The IngressClass must be set to "default"
Explanation: An Ingress resource is just configuration — it has no effect without an Ingress Controller (nginx, Traefik, etc.) to implement it. The controller watches Ingress objects and configures the actual proxy.
Q2: A NetworkPolicy selects Pods with label app=database and specifies policyTypes: [Ingress]. No ingress rules are defined. What is the effect?
- A) All traffic is allowed (no rules = allow all)
- B) All ingress traffic to database Pods is blocked ✓
- C) Only egress traffic is affected
- D) The policy is invalid and has no effect
Explanation: A NetworkPolicy with policyTypes: [Ingress] but empty ingress rules acts as a default deny for all ingress traffic to the selected Pods. This is a common way to implement default-deny policies.
Q3: Which CNI plugin should you choose if you need both pod networking AND NetworkPolicy enforcement?
- A) Flannel
- B) Calico ✓
- C) CoreDNS
- D) kube-proxy
Explanation: Flannel provides only overlay networking without NetworkPolicy support. Calico (and Cilium, Weave) implement the NetworkPolicy API. CoreDNS is DNS, and kube-proxy handles Service load balancing — they're not CNI plugins.