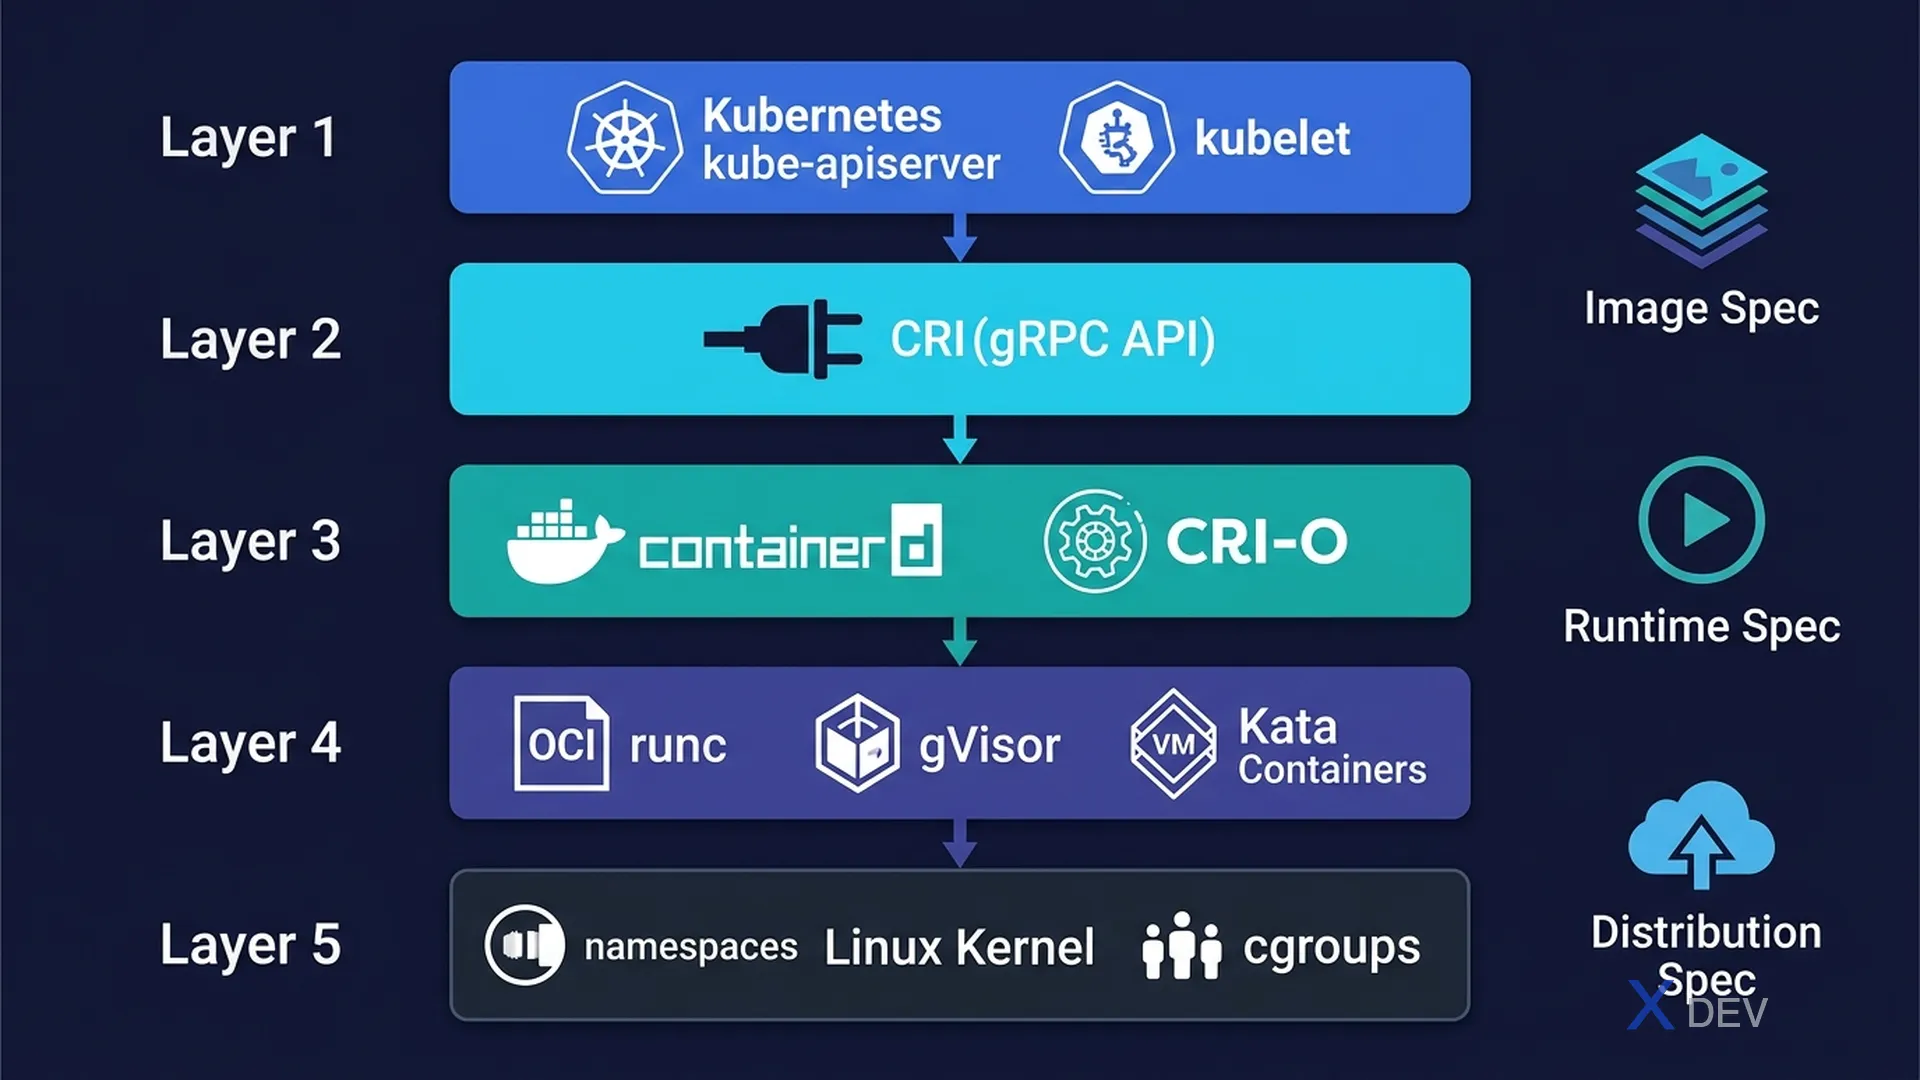
1. OCI — Open Container Initiative
OCI là tổ chức mở (thuộc Linux Foundation) định nghĩa các chuẩn mở cho containers:
| Specification | Định nghĩa | Ví dụ implement |
|---|---|---|
| OCI Image Spec | Định dạng container image (layers, manifest) | Docker image, OCI image |
| OCI Runtime Spec | Cách chạy container từ image (lifecycle, filesystem) | runc, crun, kata-containers |
| OCI Distribution Spec | API để push/pull image từ registry | DockerHub, ECR, GCR |
Exam tip: OCI standards đảm bảo interoperability: image build bằng Docker có thể chạy với containerd hoặc CRI-O mà không cần thay đổi. KCNA thường hỏi về vai trò của OCI trong cloud native ecosystem.
2. Container Runtime Interface (CRI)
Kubernetes không giao tiếp trực tiếp với Docker hay containerd. Thay vào đó, kubelet dùng CRI (Container Runtime Interface) — một gRPC API chuẩn.
Kubernetes Architecture (Runtime Layer):

  kubelet
     │ CRI (gRPC)
     ├─── containerd ─── runc ─── container
     ├─── CRI-O      ─── runc ─── container
     └─── (Docker)   ─── (deprecated v1.24+)

  OCI Runtime (runc, crun):
  - Đọc OCI runtime bundle
  - Gọi Linux kernel (namespaces, cgroups)
  - Tạo container process
3. Container Runtimes Comparison
| Runtime | Loại | Đặc điểm | Dùng trong |
|---|---|---|---|
| containerd | High-level (CRI) | Nhẹ, stable, CNCF graduated | Default Kubernetes 1.24+ |
| CRI-O | High-level (CRI) | Tối ưu cho Kubernetes, lightweight | OpenShift, Kubernetes |
| Docker Engine | High-level (non-CRI) | Deprecated từ K8s 1.24 (dùng dockershim) | Dev environments |
| runc | Low-level (OCI) | Reference OCI implementation | Backend của containerd/CRI-O |
| gVisor (runsc) | Low-level (sandbox) | Security sandbox, intercepts syscalls | GKE sandbox, untrusted workloads |
| Kata Containers | Low-level (VM-based) | VM isolation per container | Multi-tenant, high security |
Exam tip: Docker bị deprecated như Kubernetes runtime từ v1.24, nhưng Docker images (OCI-compatible) vẫn chạy được trên containerd/CRI-O. "Docker deprecated" ≠ "Docker images deprecated".
4. Container Image Layers
Layer architecture:
┌──────────────────────────────┐
│  Layer 4: App code (5 MB)    │  ← Writeable (container layer)
├──────────────────────────────┤
│  Layer 3: npm packages       │  ← Read-only
├──────────────────────────────┤
│  Layer 2: Node.js runtime    │  ← Read-only
├──────────────────────────────┤
│  Layer 1: Ubuntu base image  │  ← Read-only (shared across images)
└──────────────────────────────┘

Cache benefit: nếu Layer 1-2 giống nhau, chỉ download Layer 3-4
5. Container Registries
| Registry | Provider | Đặc điểm |
|---|---|---|
| Docker Hub | Docker Inc. | Public default, rate-limited pulls |
| ECR (Elastic Container Registry) | AWS | Private, IAM integrated |
| GCR / Artifact Registry | GCP | Private, Workload Identity |
| GHCR (GitHub Container Registry) | GitHub | Package-linked, Actions CI |
| Harbor | CNCF (open source) | Self-hosted, vulnerability scanning |
6. Cheat Sheet
| Câu hỏi exam | Đáp án |
|---|---|
| OCI định nghĩa chuẩn gì? | Image Spec, Runtime Spec, Distribution Spec |
| Default runtime K8s 1.24+? | containerd |
| CRI là gì? | Container Runtime Interface — gRPC API giữa kubelet và runtime |
| Docker deprecated trong K8s? | Từ v1.24 (dockershim removed) |
| Runtime cho untrusted workloads? | gVisor hoặc Kata Containers |
7. Practice Questions
Q1: A Kubernetes cluster uses containerd as the container runtime. A developer pushes a Docker image to Docker Hub. Can this image run on the cluster?
- A) No, Docker images are incompatible with containerd
- B) Yes, because Docker images follow OCI Image Spec and are compatible ✓
- C) Only if the cluster installs a Docker compatibility shim
- D) No, containerd only supports images from CNCF registries
Explanation: Docker images follow the OCI Image Specification, making them interoperable with any OCI-compliant runtime including containerd and CRI-O. The "Docker deprecated" refers to the runtime, not the image format.
Q2: What is the primary purpose of the Container Runtime Interface (CRI)?
- A) Define image layer formats
- B) Provide a gRPC API for kubelet to communicate with container runtimes ✓
- C) Manage container image distribution between registries
- D) Schedule containers across cluster nodes
Explanation: CRI gives kubelet a stable API to interact with different runtimes (containerd, CRI-O) without knowing implementation details. This decoupling enables switching runtimes without changing kubelet code.
Q3: Which container runtime provides VM-level isolation per container for high-security multi-tenant workloads?
- A) containerd
- B) CRI-O
- C) Kata Containers ✓
- D) runc
Explanation: Kata Containers runs each container inside a lightweight VM, providing stronger isolation than standard Linux namespace-based containers. gVisor provides user-space isolation via syscall interception, also strong but different approach.