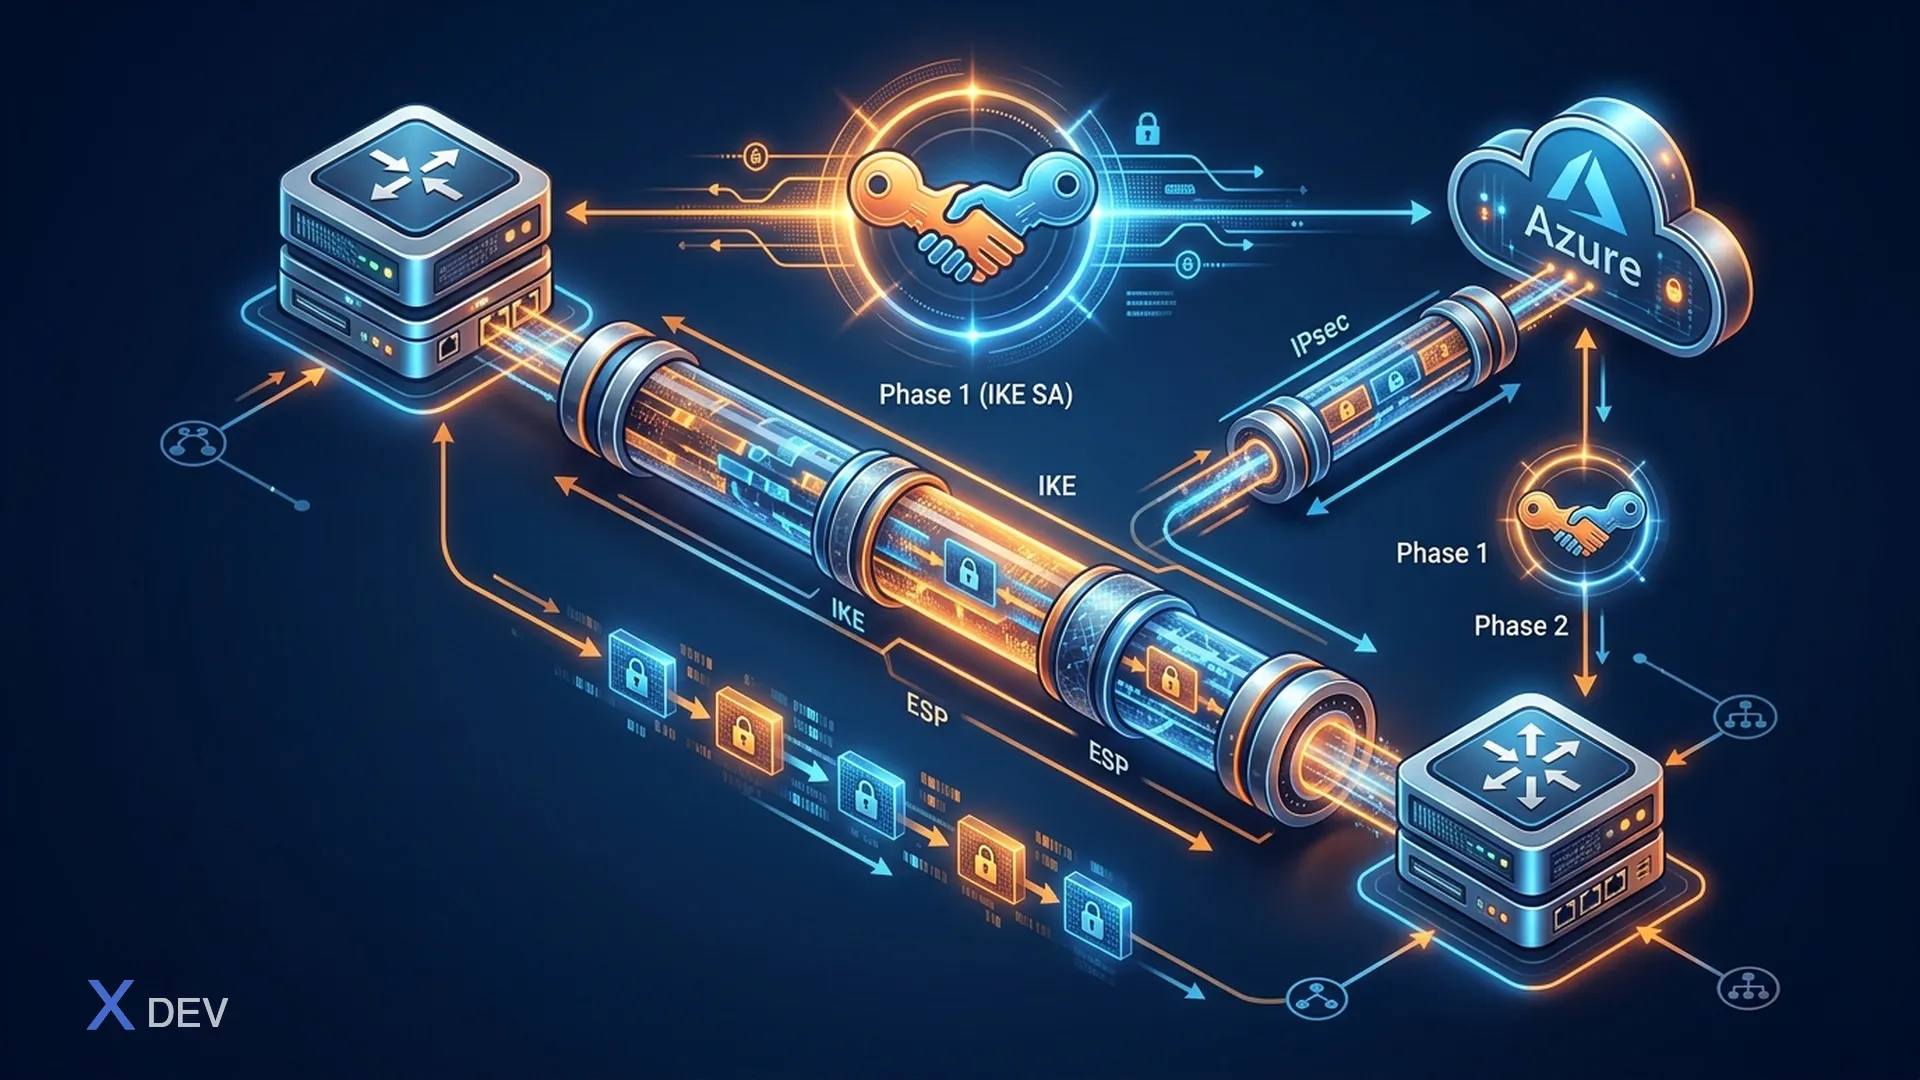
Introduction to IPsec VPN on VyOS
IPsec is the industry-standard technology for secure VPN connectivity between sites. VyOS provides complete IPsec support with IKEv2, ESP, NAT-T, and VTI. This lesson covers site-to-site configuration, policy-based vs route-based designs, interoperability with other devices, and a BGP overlay lab.
IPsec fundamentals
- IKEv2: Key negotiation protocol with stronger security than IKEv1.
- ESP: Encapsulating Security Payload for encrypted data transport.
- SA: Security Association containing per-tunnel security parameters.
- Proposal: Set of encryption and authentication algorithms.
- DH Group: Diffie-Hellman group that determines key exchange strength.
Policy-based vs Route-based (VTI) VPN
- Policy-based: Defines which traffic is encrypted by policy selectors.
- Route-based (VTI): Creates a virtual interface for flexible routing and supports dynamic protocols like BGP.
IPsec site-to-site configuration between 2 VyOS routers
# Tạo proposal set vpn ipsec esp-group ESP-GROUP proposal 1 encryption aes256 set vpn ipsec esp-group ESP-GROUP proposal 1 hash sha256 set vpn ipsec ike-group IKE-GROUP proposal 1 encryption aes256 set vpn ipsec ike-group IKE-GROUP proposal 1 dh-group 14 set vpn ipsec ike-group IKE-GROUP proposal 1 hash sha256Peer
set vpn ipsec site-to-site peer <peer-wan-ip> authentication mode pre-shared-secret set vpn ipsec site-to-site peer <peer-wan-ip> authentication pre-shared-secret '<secret>' set vpn ipsec site-to-site peer <peer-wan-ip> ike-group IKE-GROUP set vpn ipsec site-to-site peer <peer-wan-ip> esp-group ESP-GROUP set vpn ipsec site-to-site peer <peer-wan-ip> local-address '<local-wan-ip>' set vpn ipsec site-to-site peer <peer-wan-ip> tunnel 1 local prefix '192.168.1.0/24' set vpn ipsec site-to-site peer <peer-wan-ip> tunnel 1 remote prefix '192.168.2.0/24'
Route-based VPN with VTI
set interfaces vti vti0 address '10.100.100.1/30'
set vpn ipsec site-to-site peer <peer-wan-ip> vti bind vti0
set vpn ipsec site-to-site peer <peer-wan-ip> vti esp-group ESP-GROUP
set vpn ipsec site-to-site peer <peer-wan-ip> vti ike-group IKE-GROUP
IPsec interop with Cisco/Palo Alto
Synchronize proposals, pre-shared key, and local/remote subnets. Ensure NAT-T is enabled if NAT exists in the path.
Route-based VPN to Azure with BGP
set interfaces vti vti1 address '169.254.21.2/30'
set protocols bgp 65001 neighbor 169.254.21.1 remote-as 65515
set protocols bgp 65001 neighbor 169.254.21.1 update-source vti1
DMVPN dual-hub concept
VyOS supports DMVPN with multiple hubs to improve availability. The configuration is similar to route-based VPN, with additional peers.
IPsec verification and troubleshooting
show vpn ipsec sa
show vpn ipsec status
run monitor vpn ipsec
Debug a peer if the tunnel does not come up:
run monitor vpn ipsec log peer <peer-wan-ip>
Hands-on lab: Route-based IPsec VPN with BGP overlay
- Configure VTI interfaces on both VyOS routers.
- Configure IPsec peers, proposals, and pre-shared key.
- Set up BGP on the VTI interfaces for route exchange.
- Verify tunnel and routing status.
# Kiểm tra trạng thái IPsec
show vpn ipsec sa
# Kiểm tra VTI interface
show interfaces vti
# Kiểm tra BGP
show ip bgp summary
Summary
This lesson gives you a practical understanding of IPsec on VyOS, policy-based vs route-based designs, interoperability, BGP overlay labs, and real-world troubleshooting skills.